Multi-agent orchestration is the coordination of several specialized AI agents so they work together on one goal. An orchestration layer decides which agents are needed, splits the work into steps, passes context between them, handles errors and enforces permissions, then combines the results. Instead of one agent trying to do everything, each agent masters a narrow job and the orchestration layer ties them together.
This guide explains how multi-agent orchestration works, the main orchestration patterns, why it beats a single agent for complex work, and the challenges that matter most in an enterprise: permissions, memory, observability, agent-to-agent communication and cost. It zooms in on one of the seven tenets of AI orchestration.
A multi-agent system is a set of AI agents that work together toward a goal. An agent is an autonomous software entity that can perceive its environment, make decisions and take actions. Most "agentic workflows" in use today are still single-agent and siloed. Multi-agent systems are a newer frontier, and orchestration is what makes them reliable.
Agents decide based on context, and in a large company it's easy for one agent to get lost in an overwhelming amount of it. Imagine a single employee who had to know every internal policy, every Salesforce record, every engineering ticket and every file in Google Drive. They couldn't function. An agent is the same: it needs context to perform, but with too much of it, it starts to conflate things.
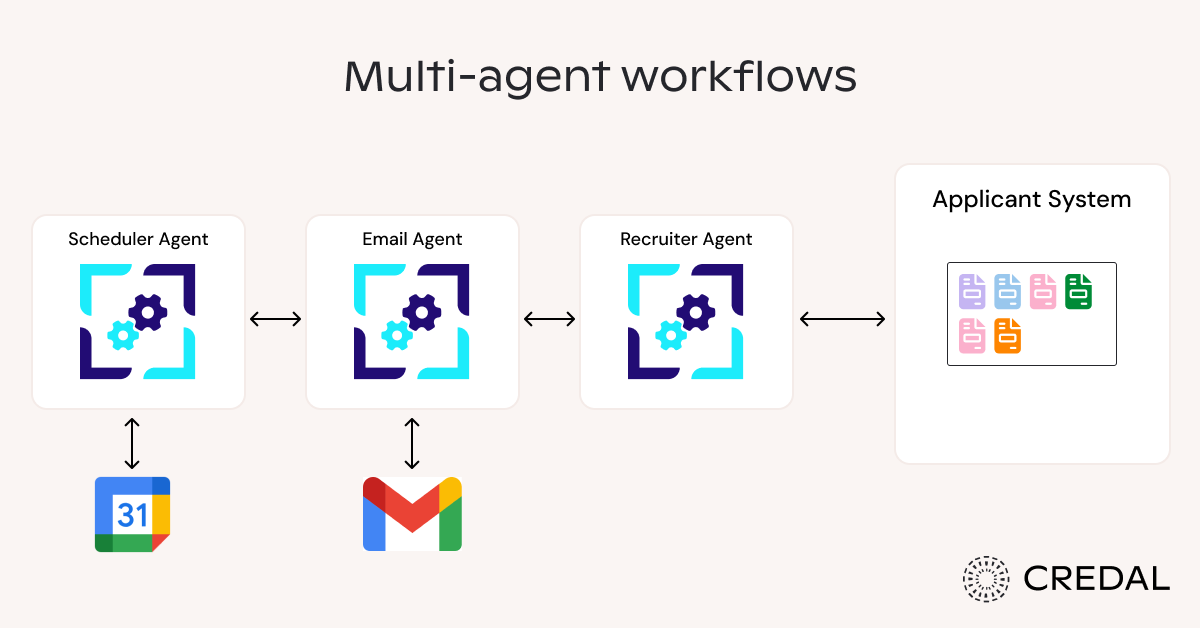
In short, multi-agent orchestration rests on two ideas: specialization over do-everything agents, and cross-agent communication to get work done.
An Applications Evaluator Agent reviews each candidate. For promising ones it works with an Email Outreach Agent and a Scheduler Agent to book an interview. The evaluator focuses on judgment while the other two make sure the company's voice and calendars are used.
An Intent Classifier Agent routes each issue to a Knowledge Base Retrieval Agent and delegates fixes to a Remediation Agent, which checks a Policy Guard Agent that knows the business's rules. Ticket updates are published to subscribers, and destructive remediation actions require human approval.
A Report Compiler Agent works with an Anomaly Detector Agent and an Account Owner Notifier to catch irregularities and alert the right people. Outreach is rate-limited so account owners aren't overwhelmed, and every monitoring action is logged.
Looking for more workflow ideas, or for how to compare platforms? See our guide to multi-agent platforms.
Three of the seven orchestration tenets become much harder with several agents: permissions, memory and observability.
A core rule of safe agents is that an agent inherits the permissions of whoever dispatched it. If the user can see X, so can the agent. If the user can't see Y, neither can the agent, or it might leak Y to them. With one agent, permission mirroring handles this. With several, it gets harder:
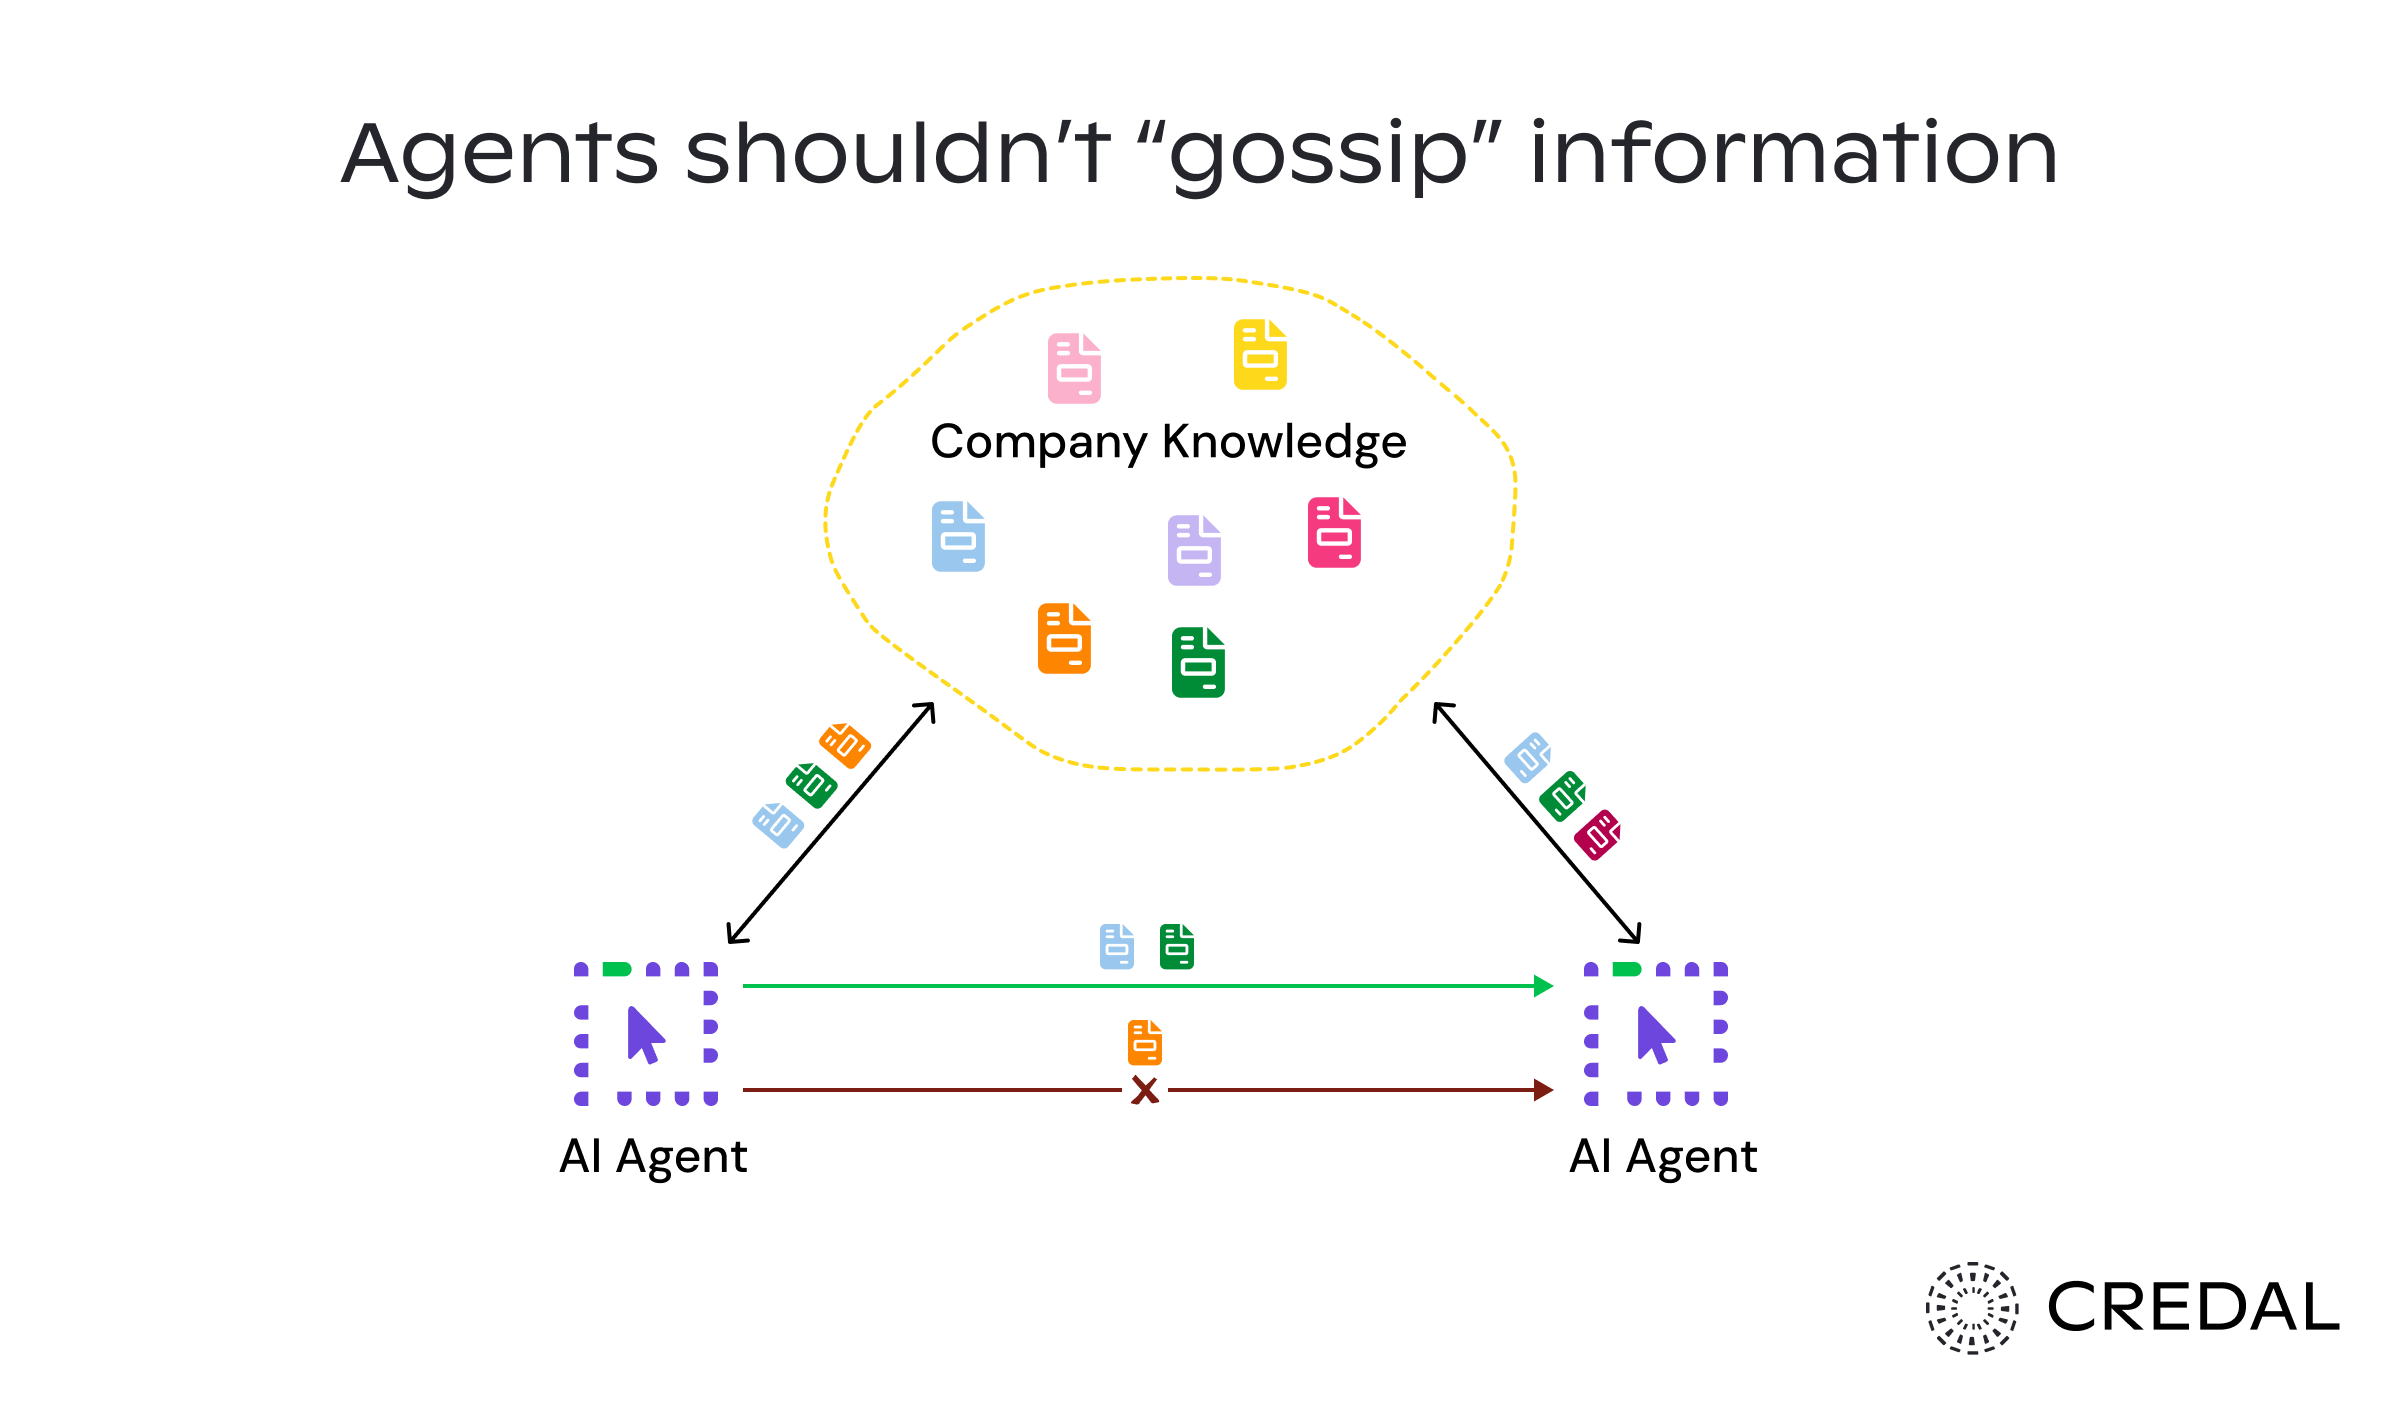
The fix is that agents must not "gossip." They should share only information both sides have mutual access to, and must not tap earlier memory that could carry a leak. Four rules put that into practice:
Requiring human approval before an agent contacts one it hasn't worked with before is a useful extra safeguard, but it doesn't replace the four rules.
Does this limit what agents can do? Yes. The organization has to design permission mirroring to maximize context and collaboration without causing a leak. It's a non-negotiable constraint, since regulations like GDPR and CCPA and standards like PCI DSS penalize failures of data custody.
For a single agent, observability means tracking its reads and writes. With several, you also need to follow the paths between agents, much as distributed systems trace a request through every service it triggers. You need to know who called whom, with what context, and which tools or actions were invoked.
An effective setup includes trace IDs, a span for each agent and action, decision logs (including permission checks), data access logs, and cost and latency metrics. It should support two views: a trace view to debug individual sessions, and a topology view that shows which agents collaborate, which paths are busiest and where bottlenecks form.
This matters for compliance (frameworks like SOC 2 and PCI DSS expect you to trace sensitive data through a system), for security (reconstructing an incident) and for debugging. See our guide to AI audit logs for what to capture.
Memory, permissions and observability are problems single agents share. Getting agents to work together is a uniquely multi-agent problem.
A2A (Agent2Agent) is an open protocol, introduced by Google and now hosted by the Linux Foundation, that standardizes how agents talk to each other through structured messages with task specifications, context pointers and correlation IDs. When agents work together, familiar network problems appear: retries, timeouts and idempotency (making sure duplicate actions don't happen). A shared protocol helps handle them gracefully. Read more in what A2A is and what happened to it. Whichever protocol you choose, an orchestration platform should support A2A or an equivalent so agents can communicate without breakage.
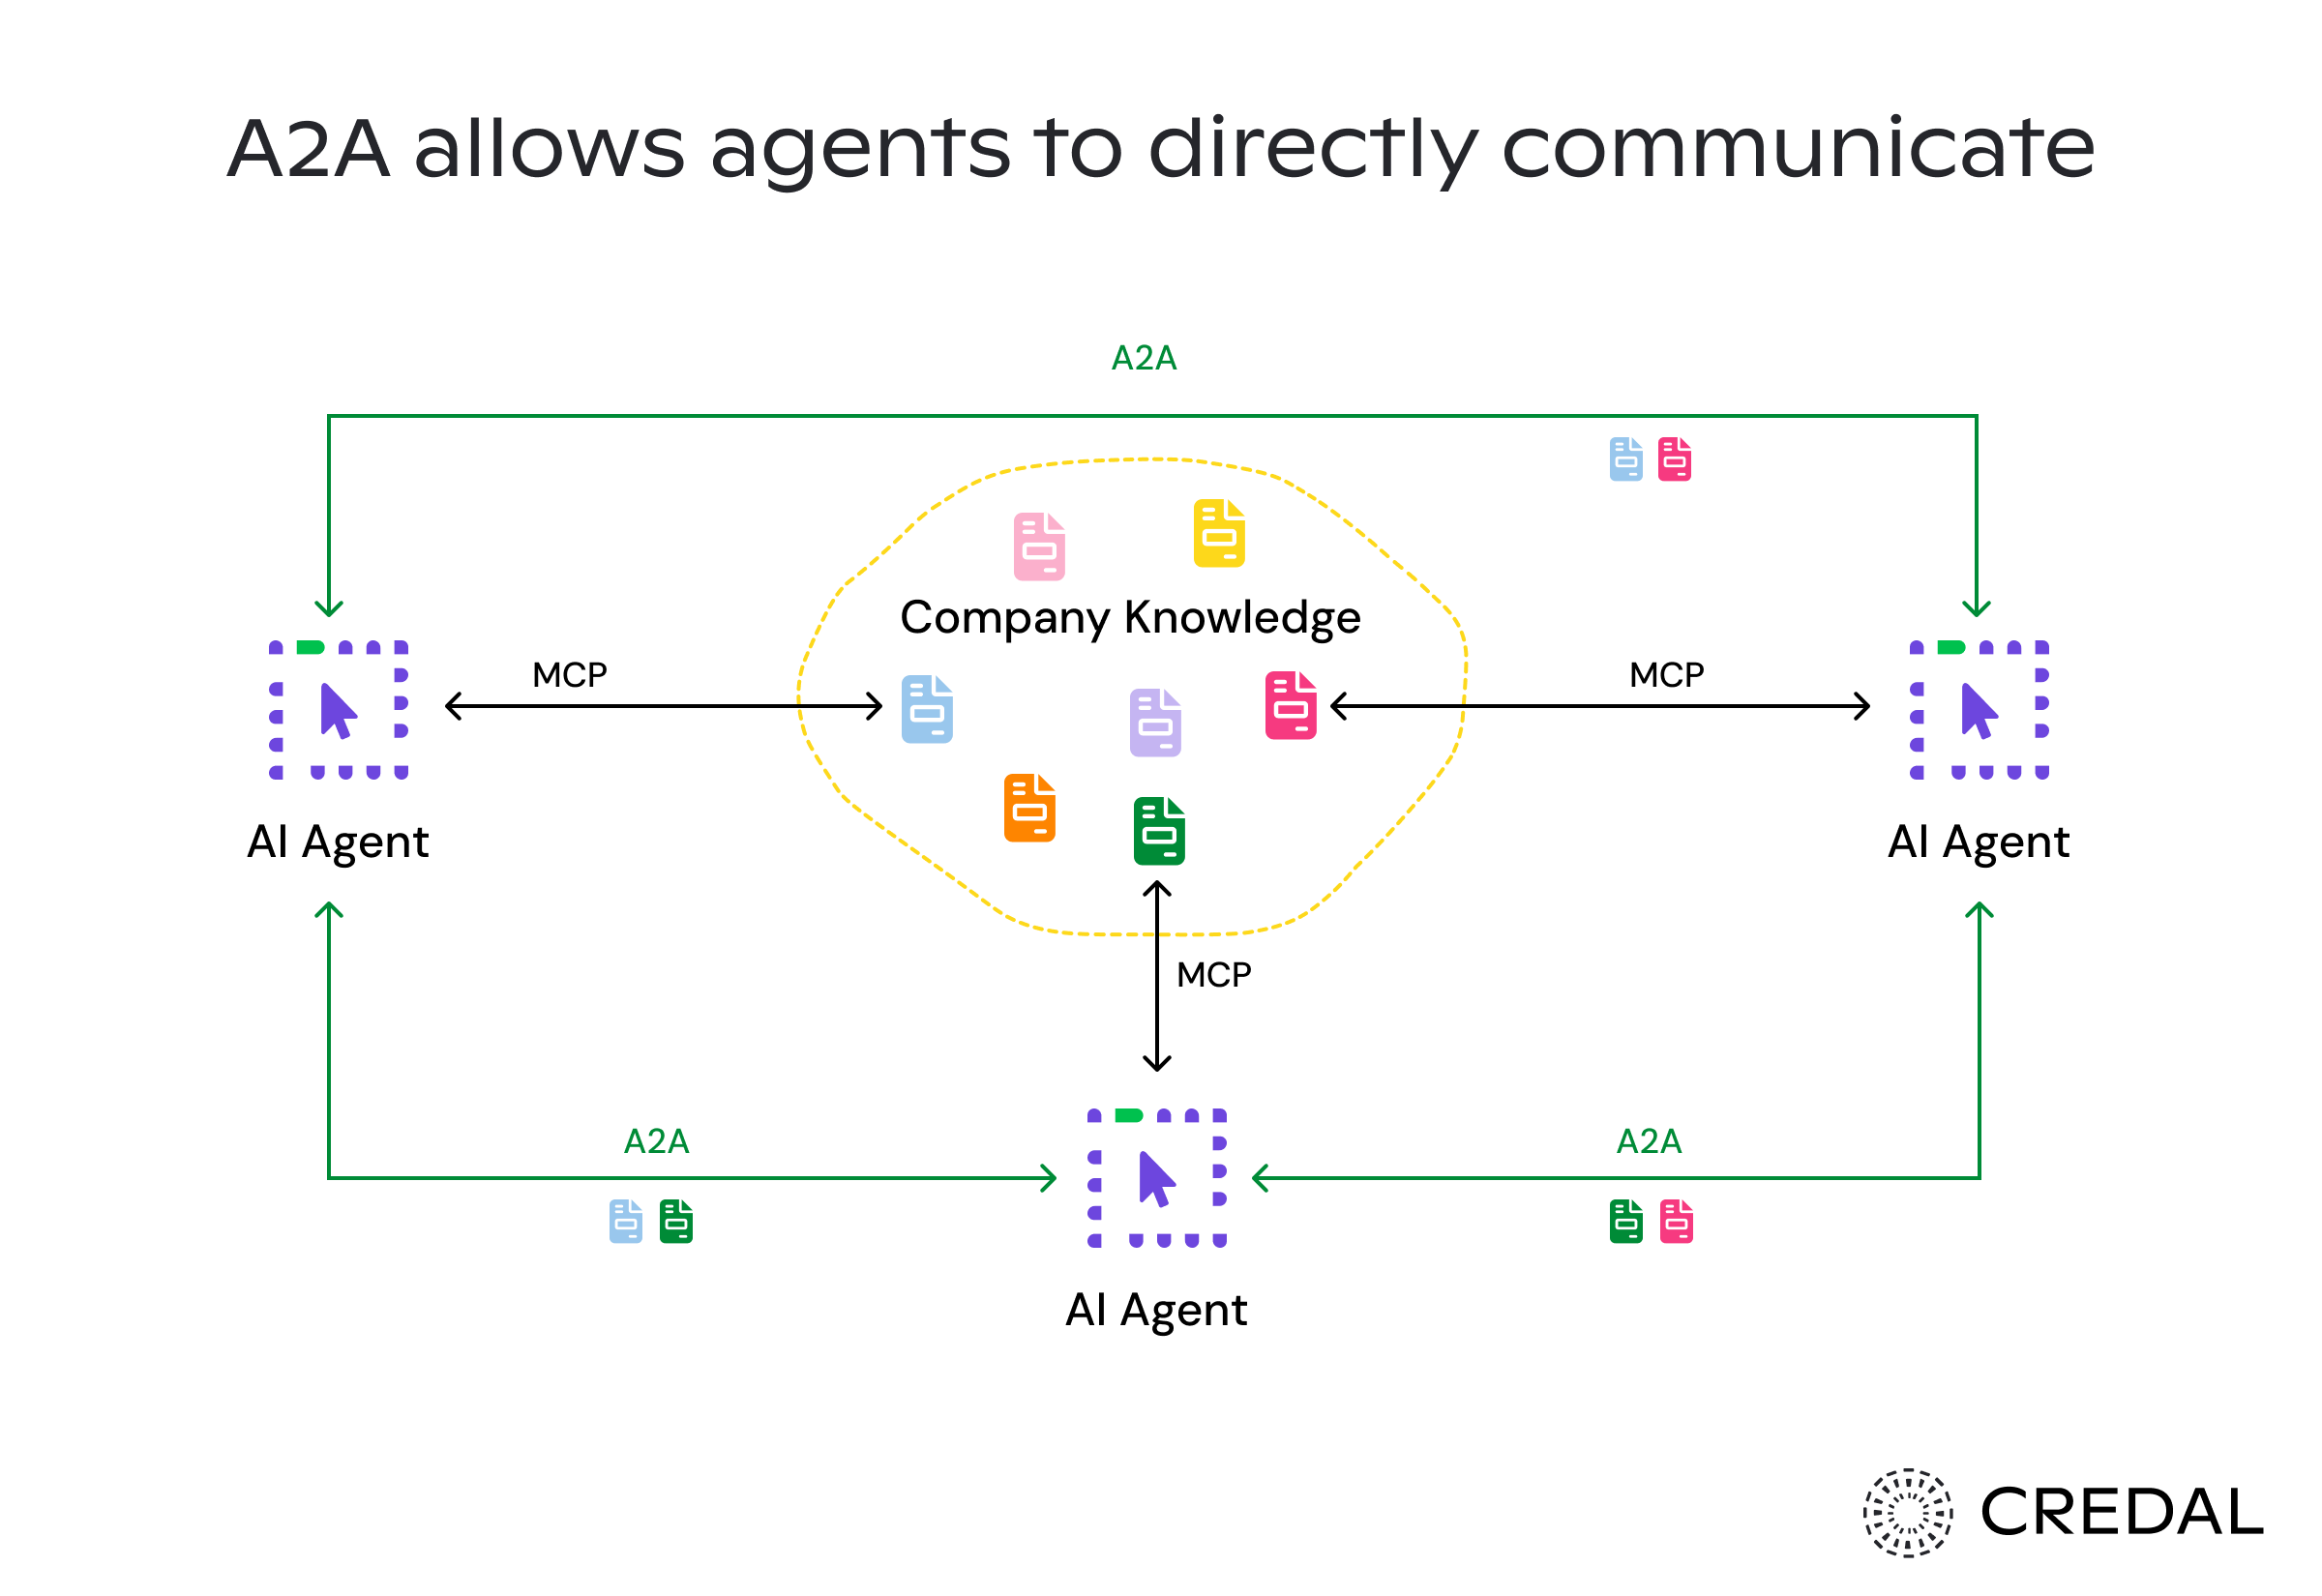
Wiring agents together by hand is slow and turns multi-agent workflows into fancy Zapier chains. That suits deterministic jobs, but agents should be able to discover each other and decide what to use, especially for research-heavy tasks where information sits in many places. A good platform exposes agents to one another through an agent registry where each agent has a profile documenting what it is for. The same registry is what stops agent sprawl.
Many workflows run best with an orchestrator agent that connects and delegates, like a human manager. It reduces the discovery problem and redundancy by acting as a source of truth (the hub and spoke model). Technically it is an ordinary agent: it communicates through A2A or an equivalent, keeps memory for context and runs on an LLM. The platform's job is to make its traces and data easy to find, because that's where a developer will look first when something goes wrong.
What about security for the orchestrator agent? Because the orchestrator can delegate to many agents, it should hold no more access than the person it acts for, should not be able to hand out permissions it lacks, and its delegations should be logged and, for sensitive actions, approved by a person.
Costs grow with the number of agents. Each one runs on an LLM with token costs, and complex workflows can involve many API calls. A platform should flag when spend, call volume or latency crosses a threshold so a person can review it, and rate-limit agents so a loop can't run up a large bill.
A framework is a code library developers use to define agents and their coordination. A platform adds what an enterprise needs around it: connectors, hosting, per-user permissions, approvals, logging, cost controls and a registry, usually with a way for non-engineers to build agents. If agents will touch sensitive data or change business systems, make sure those enterprise pieces exist before you scale.
Credal is a governed platform for AI agents. Teams build agents with the Agent Builder, connect them to systems like Snowflake, Google Drive, Salesforce and Jira through governed MCP servers on the MCP Platform, and run several agents that discover and work with one another.
Multi-agent workflows need care. To see how Credal handles them, get a demo.
The coordination of several specialized AI agents toward one goal, with an orchestration layer that assigns work, shares context, handles errors and enforces permissions.
They let developers define agents, tools and the rules for how agents hand work to each other, using patterns such as sequential, concurrent, hierarchical or handoff. A framework supplies the coordination logic. Security, logging and hosting are usually left to you.
Narrow, specialized agents are more accurate than one agent holding all the context, they can reuse each other's skills, and each can have its own limited permissions.
Higher accuracy, reuse of agent skills, a smaller blast radius for mistakes, easier scaling to new workflows and the ability to have one agent check another's work.
An agent that acts like a manager. It receives a request, decides which agents are needed, delegates sub-tasks and combines the results. It runs like any other agent, on an LLM and with memory, and communicates with other agents through a protocol such as A2A.
Have every agent inherit the permissions of the person it acts for, share only data both agents may see, partition and tag memory, log every handoff and approval, and require human approval for high-risk actions.
Multi-model orchestration routes requests between different AI models, for example picking the best model for each task. Multi-agent orchestration coordinates agents that each have their own tools, context and permissions. The two are often combined, since each agent can use a different model.
Permission and memory leaks between agents, tracing paths across agents, standardizing agent-to-agent communication, helping agents discover each other, and controlling cost and latency as the system grows.

One platform for all agents. Full visibility for admins, full access for teams.

One platform for all agents.
Full visibility for admins, full access for teams.